Enterprise Voice AI Agents Security: How Ringg Protects Every Conversation
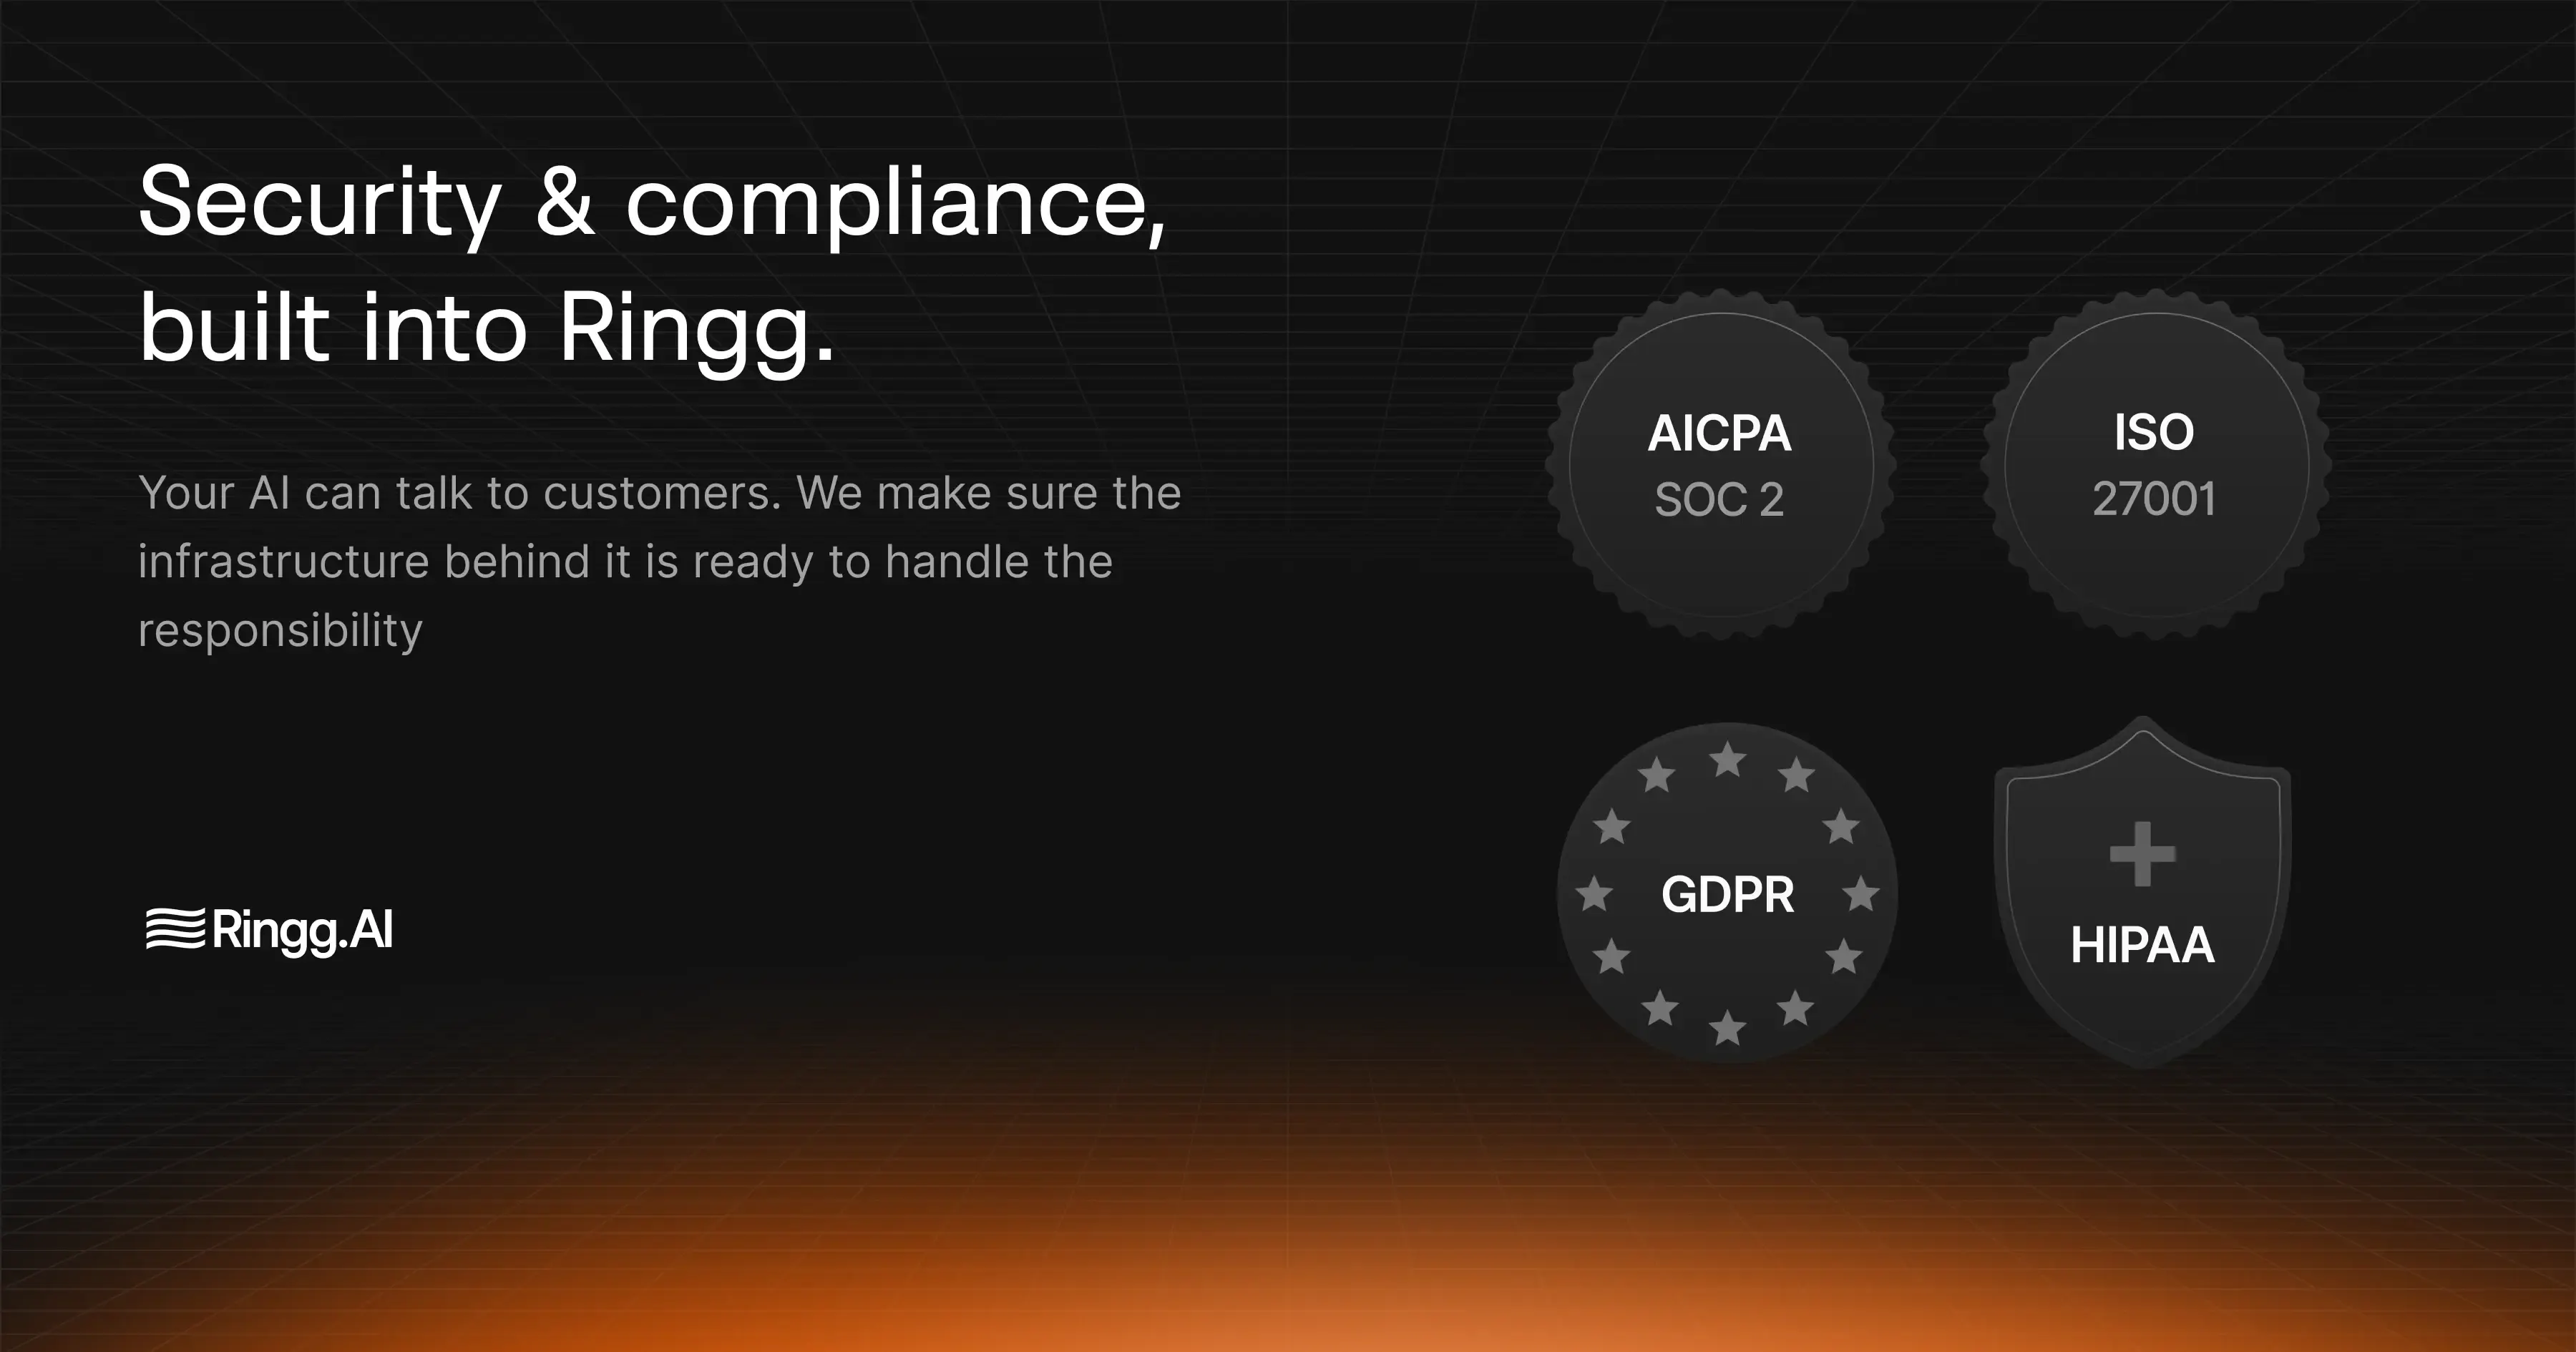
Ringg AI is built for secure inbound and outbound enterprise calling and is SOC 2 Type II, ISO 27001, HIPAA, and GDPR-compliant.


Key Takeaways
- Enterprise voice AI security must protect the complete call lifecycle, from audio capture and processing to integrations, storage, access, and deletion
- Ringg AI is compliant with SOC 2 Type II, ISO 27001, HIPAA, and GDPR.
- Ringg does not use customer data to train AI models and supports secure transmission, controlled access, responsible retention, and customer-requested deletion.
- A secure deployment combines Ringg’s platform controls with appropriately configured permissions, integrations, human escalation, and organisational policies.
Enterprise voice AI agents handle more than spoken words. A single conversation may produce customer identifiers, appointment details, account information, and actions inside connected business systems.
That makes security a fundamental requirement for deploying voice AI at scale.
Ringg AI is built for secure inbound and outbound enterprise calling. The platform is SOC 2 Type II, ISO 27001, HIPAA, and GDPR compliant.
Why Enterprise AI Voice Agent Security Matters
Voice AI connects several technologies in real time. These can include telephony, speech recognition, AI reasoning, voice generation, CRM software, payment systems, scheduling platforms, and internal databases.
During a call, a customer might provide:
- Personal and contact details, such as names, phone numbers, email addresses, and delivery addresses
- Account, order, and authentication information
- Health, prescription, financial, or insurance information
- Customer history and other confidential business information
The security question is therefore not limited to whether the phone call itself is protected. Enterprises must understand how information is captured, transmitted, processed, accessed, retained, shared with connected systems, and eventually deleted.
This lifecycle approach is consistent with established security frameworks. The National Institute of Standards and Technology recommends managing AI risk throughout the design, development, deployment, and use of AI systems. OWASP also identifies prompt injection and sensitive-information disclosure as important risks for applications built with large language models.
How Data Moves Through an Enterprise Voice AI Call
A voice conversation feels like one interaction to the caller, but multiple controlled steps may occur behind the scenes.
1. The call enters the telephony layer
The caller connects to the organisation through its chosen telephony infrastructure. The system receives the audio stream and the information required to route the call.
2. Speech is converted into text
Speech-recognition technology processes the audio so the AI agent can interpret the caller’s request. This stage may involve personal or regulated information, so transmission security, approved providers, and clear retention decisions matter.
3. The AI agent determines the next action
The agent evaluates the conversation within the permissions and workflow configured by the business. It may answer a question, retrieve approved information, collect structured details, or initiate an authorised action.
4. Connected systems complete the workflow
When a task requires a CRM, scheduling platform, payment system, or internal database, the agent sends only the information needed for the approved operation. Credentials should remain on the server side, and access should be limited to the records and actions required for that workflow.
5. The agent produces a spoken response
The approved response is converted back into speech and returned to the caller. Output controls and human escalation are important when a request is sensitive, ambiguous, or outside the agent’s authority.
6. Approved records may be retained
Depending on the use case and customer configuration, the workflow may create recordings, transcripts, summaries, call metadata, or updates in connected systems. Enterprises should define which records are necessary, who can access them, how long they are retained, and when they are deleted.
How Ringg Protects Enterprise Voice Conversations
Ringg applies security controls across the infrastructure, product, and operational layers of an AI call.
Secure data transmission
Ringg’s production guidance requires API communication over HTTPS. This protects information while it moves between authorised systems and reduces the risk of interception during transmission.
Customers should also secure their side of the connection by protecting credentials, restricting origins, validating connected domains, and limiting access to trusted systems.
Encryption at rest
Ringg’s Trust Center states that production databases storing customer data are encrypted at rest. Together with HTTPS and TLS for transmitted data, this protects customer information while it moves between authorised systems and while it is stored in Ringg’s production environment.
Secure credential management
Ringg recommends that customers:
- Store API keys in secure server-side systems
- Limit which users and services can access credentials
- Rotate credentials if exposure is suspected
- Monitor unusual API usage
- Apply the principle of least privilege
These practices help reduce the damage that could result from an exposed or misused credential.
Security logging, backups, and incident readiness
Ringg's Trust Center documents the centralised collection of security events for critical systems, review of anomalous or suspicious activity, regular backups with integrity testing, and formal incident-management and vulnerability-management procedures. It also publishes a web application VAPT closure report.
Customer data is excluded from AI model training
This applies to customer conversations and other data processed through the customer’s Ringg implementation. Excluding customer information from model training helps maintain a clear boundary between operating an enterprise workflow and improving general-purpose AI models.
This is particularly important when conversations may contain personal, financial, health, or confidential business information. OWASP recommends preventing sensitive user information from entering model-training data as part of reducing sensitive-information disclosure risk.
Data retention and deletion
Different enterprises have different legal, contractual, and operational requirements for retaining call data.
Organisations should determine:
- Whether recordings are required
- Whether transcripts or summaries need to be retained
- Which users should have access
- How long each type of record should remain available
- When data should be deleted
Ringg is GDPR compliant. Its approach to retention and deletion supports GDPR principles such as data minimisation and storage limitation, which require personal information to be limited to what is necessary and retained only as long as needed.
Security Evidence Enterprise Buyers Can Review
Security claims are more useful when buyers can inspect the evidence behind them. Ringg’s public Trust Center gives enterprise teams a central place to evaluate its compliance posture, monitored controls, policies, subprocessors, and available reports.
The Trust Center includes a web-application VAPT closure report; policies covering encryption, access control, incident management, data retention, vulnerability management, vendor management, and business continuity; and monitored controls covering areas such as production access, security-event logging, backups, and vendor oversight.
Enterprise security teams can review the Ringg Trust Center or contact Ringg when they need applicable reports and documentation for a vendor assessment.
An Enterprise AI Voice Agent Security Checklist
Before selecting or deploying an AI voice agent, ask the vendor:
- Is customer data used to train AI models or improve general-purpose models?
- How are audio, transcripts, summaries, metadata, and production databases encrypted?
- Who can access production systems and call data, and how often is access reviewed?
- What security events are logged, monitored, and investigated?
- How are retention, data-subject requests, and deletion handled?
- Which subprocessors handle customer information, and how are they assessed?
- What do the vendor’s SOC 2 report, ISO certificate, HIPAA terms, BAA, and GDPR documentation cover?
- How are vulnerabilities, incidents, backups, recovery, and high-risk agent actions managed?
Broad claims such as “enterprise secure” or “fully compliant” are not sufficient on their own. Security teams should review the applicable reports, scope, contractual terms, data flow, controls, and implementation requirements.
BOOK A DEMO
Ready to deploy secure, enterprise-grade voice AI?
See how Ringg AI helps teams launch reliable voice agents with enterprise security and compliance built in.
Source Citations
- National Institute of Standards and Technology. AI Risk Management Framework.
- OWASP GenAI Security Project. Sensitive Information Disclosure.
- Cybersecurity and Infrastructure Security Agency. Zero Trust Maturity Model.
- European Union. General Data Protection Regulation (EU) 2016/679.
- AICPA & CIMA. System and Organization Controls Suite of Services.
- International Organization for Standardization. ISO/IEC 27001:2022 Information Security Management Systems.
- US Department of Health and Human Services. The HIPAA Security Rule.
- OWASP GenAI Security Project. Prompt Injection Risks and Mitigations.
Frequently Asked Questions
AI voice agents can be used securely when the entire workflow is protected, including telephony, speech processing, AI models, integrations, storage, and administrative access. Enterprises should evaluate the complete data flow rather than relying on the security of one model or provider.
Related blogs
View all blogs
Voice AI Guides
What is an AI Voice Agent? Definition, Features, Benefits, Use Cases and Examples
Stop losing customers to long hold times. Discover how an AI voice agent transforms telephone support and scales enterprise operations instantly.
07 Jul 2026 · 14 min read

Voice AI Guides
Voice AI Technology in 2026: How AI Assistants Transform Speech-to-Conversation
Convert words into natural conversations using speech-to-conversation AI in 2026. Explore the architecture, process, and applications of voice AI technology.
06 Jul 2026 · 7 min read
Voice AI Guides
A Guide to Evaluating AI Voice Agents in 2026
Don't fall for the “Golden Demo.” Learn the 5 pillars for evaluating AI voice agents, from latency & ROI to agility & integrations.
07 Jul 2026 · 6 min read